
Applications
Smart locks for data centers: every rack door with a reason and a record
Zoned credentials from perimeter to cage to rack, tamper-evident audit trails, offline resilience and a rollout aligned to documented facility standards.
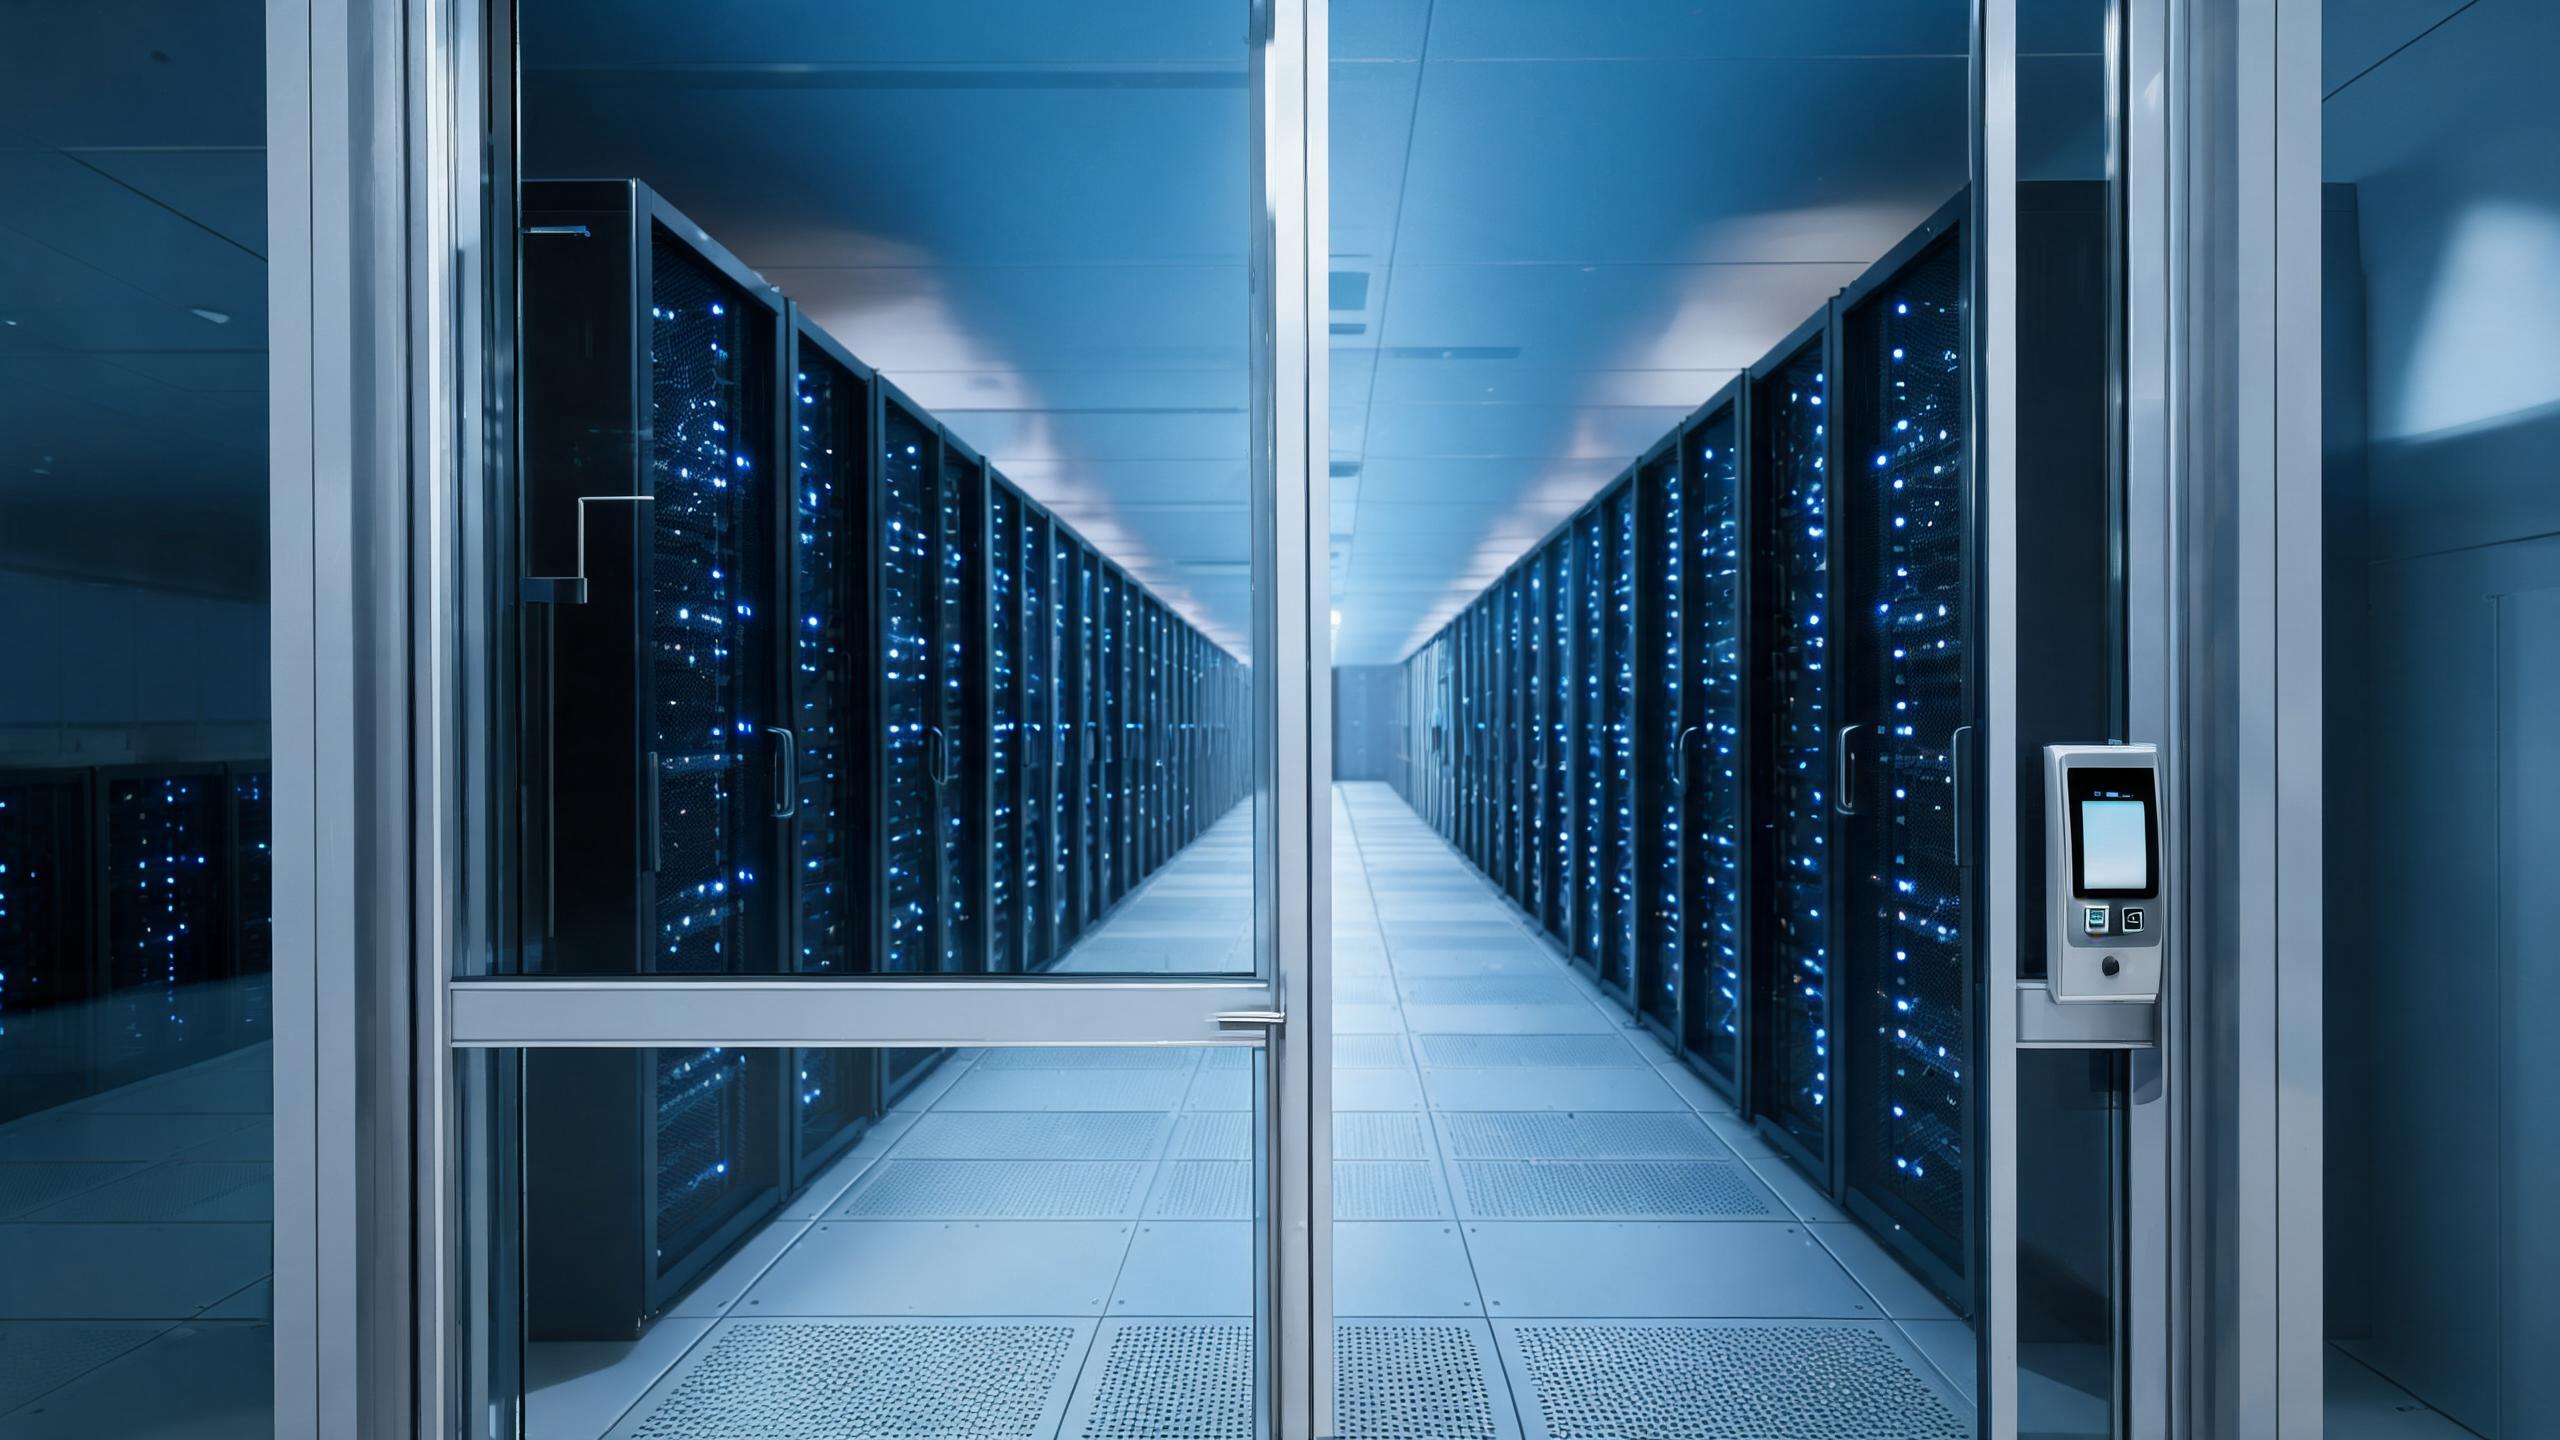
Data center security is concentric: perimeter, building lobby, data hall, cage and rack, and the access program has to prove who crossed each layer. Smart mechanical and electronic locking at doors and racks contributes identity, scheduling and an audit trail that survives audits by customers, insurers and compliance reviewers — which is why data center buyers care more about evidence, documentation and tested behavior than about a feature list on a lock. Hardware is specified for offline resilience, long service intervals and maintenance procedures that do not compromise adjacent racks, and integration with the named access platform and ticketing system is scoped in writing. Nothing in a data center specification is implied from marketing language. The standards page explains how documented requirements drive hardware selection, the certifications overview covers what evidence to request, and the telecom page covers unmanned remote shelters.
Data center access at a glance
| Security layers | Perimeter, lobby, data hall, cage and rack each carry distinct credentials, never one universal badge |
| Audit evidence | Door and rack events support customer, insurer and compliance audits, with records retained per facility policy |
| Resilience | Doors and rack locks remain operable through network outages on cached credentials and mechanical procedures |
| Change control | Installation and battery service follow ticketed maintenance windows rather than ad-hoc technician visits |
| Hardware duty | Long-service, low-maintenance platforms chosen for conditioned but demanding data-hall environments |
| Integration | Access, ticketing and monitoring systems are scoped against the named platforms and versions in writing |
| BOM shape | Cage and rack locks by inventory, door controllers, credential hardware, audit tooling and staged spares |
Answer unit
Rack-level electronic locks or cage-and-door control only?
Colocation and multi-tenant halls increasingly lock the rack itself; single-owner enterprise rooms may stop at the cage. The tenant model decides.
| Dimension | Cage and hall doors only | Electronic locks at the rack row |
|---|---|---|
| Granularity | Control at cage boundary | Control and record at each cabinet |
| Tenant separation | Trust inside the shared cage | Individual customer cabinets isolated within a cage |
| Service workflow | Escort required for rack work | Ticket-scoped credentials open only the assigned rack |
| Audit depth | Hall and cage events | Per-cabinet event history for customer reports |
| Hardware count | Modest door-level count | High count of rack-specific locks and keys |
| Typical fit | Single-owner enterprise data halls | Colocation, retail colocation, managed services |
Door types and lock-body match
Rack form factors and fire-rated hall doors define separate hardware tracks; surveys run cabinet by cabinet.
| Opening | Typical door | Lock approach |
|---|---|---|
| Data hall entrance | Fire-rated security door, mantrap or interlock | Card and optionally multi-factor reader with mantrap logic coordinated to the system |
| Cage door | Mesh security cage with frame lock | Reader and monitored electric release integrated with cage alarming |
| Server cabinet | Standard 19-inch rack with hinged door | Rack-specific electronic handle or cabinet lock keyed to ticketed access |
| CRAC / electrical room | Metal service door | Facilities-only credential with entry records and override |
| Loading and receiving | Industrial overhead or security door | Escort and delivery-window access distinct from hall credentials |
| Break-glass / egress | Fire-rated exit hardware | Life-safety devices untouched by the access overlay per the fire schedule |
Example BOM shape for a colocation hall
This example illustrates a typical configuration, not a specific customer project. Cabinet count and the tenant model drive the list.
| Component | Typical logic | Notes |
|---|---|---|
| Hall and cage controls | Readers, controllers and releases at perimeters | Specified with mantrap and alarming behavior in writing |
| Rack locks | One electronic lock per secured cabinet | Handle type matched to the actual rack series |
| Credential system scope | Badge, factor and policy integration work | Named platform, version and ticket flow confirmed in writing |
| Resilience provisions | Offline-capable controllers and documented mechanical path | Tested in a simulated outage before acceptance |
| Staged spares | Rack locks, controllers and readers held on site | Swap procedures written for maintenance windows |
How a data center program rolls out
- Requirements and inventoryDocumented standards, rack series, door schedules and platform names are gathered before any hardware is named.
- Evidence reviewPer-SKU technical evidence and test behavior are reviewed against the facility control set and customer audit needs.
- Pilot cageOne cage runs real ticketed rack access, outage simulation and audit export before hall-wide rollout.
- Phased deploymentCages commission without live-rack disruption, using maintenance windows and chain-of-custody for old keys.
- Assurance handoverProcedures, audit playbooks, spare locations and response paths are handed to security and facilities teams.
Related applications
Related critical-facility pages
Smart locks for data centers: common questions
What access evidence does a data center audit expect?
Auditors and colocation customers look for a defensible chain: a defined zone model, credentials issued under least privilege, a reason or ticket tied to sensitive entries, retained event records, and proof that removal of access actually happens when staff or contracts change. The lock hardware contributes the door and rack events, but the evidence only works when policy, platform and hardware align, which is why the named access system and retention policy are scoped in writing before hardware is ordered. Generic “bank-grade” claims are not treated as evidence.
Do rack locks work when the network is down?
Critical facilities require offline resilience as a design condition: controllers and rack locks honor cached credential decisions through outages, emergency mechanical procedures remain available, and events buffer locally and reconcile when connectivity returns. The pilot cage includes an actual network-loss test rather than a paper assumption. Battery and maintenance schedules avoid putting racks in an unknown state, and every degraded-mode behavior is documented in the runbook so security staff are not improvising during an incident.
How are technicians given access to one specific rack?
Ticketed access issues a credential scoped to the named cabinet and the work window, so a colocation engineer cannot open adjacent customer racks even inside the shared cage; escort rules layer on top where the lease requires them. When the ticket closes the credential dies automatically, and the cabinet record shows the work window. This contrasts with master keys that open entire rows silently. The workflow is integrated with the named ticketing system within a scope agreed in writing, including what happens for emergency break-fix outside normal approvals.
Can electronic rack locks be added to existing cabinets?
Many standard rack series accept electronic handles or cabinet locks without replacing the cabinet, but the rack manufacturer, door style and existing handle are inventoried first because retrofit kits are series-specific. Pilot installation on each cabinet type validates fit and the maintenance path before hall-wide deployment, and installation happens inside change windows with a record for every rack touched. Mixed inventories commonly end with two or three approved kits rather than one product across the hall.
How is a data center BOM and MOQ scoped?
The BOM separates perimeter and cage controls, rack locks by cabinet series, integration scope, resilience provisions and staged spares, with MOQ and lead time confirmed in writing per quotation after the requirements review. Compliance-driven programs usually begin with one pilot cage and a defined acceptance test before the volume commitment. Send the rack inventory, door schedule, named platforms and the applicable documented standards, and the quote maps hardware to each security layer rather than counting undifferentiated locks.
Specify rack access your auditors can actually verify
Send the rack inventory, door schedule, named platforms and applicable standards — receive a layer-mapped BOM with pilot scope and written MOQ and lead-time terms.
Discuss your project (RFQ)Project configurationsLast updated: October 31, 2026 · Reviewed by the Smart Lock Factory editorial team